Hrishikesh Patra, Cybersecurity Consultant (Web, API & Android Security)
About Me
Identification
I'm Hrishikesh Patra, a Cybersecurity Professional
I'm a Security Consultant and Penetration Tester with 4+ years of experience in vulnerability assessment and penetration testing across web, API, Android, and network environments. At EY Global Delivery Services, I work with banking, telecom, and media clients to identify security risks and deliver clear, evidence-based remediation guidance, and I don't just hunt for vulnerabilities, I build the AI-driven tooling that helps find them faster.
Beyond client engagements, I build security tools, contribute to open-source projects, and continue growing my expertise in AI security, currently working toward INE's AI Systems Security Specialist (eAIS) certification. My work has been recognized through NCIIPC's Responsible Vulnerability Disclosure Program and acknowledged by CERT-In for responsible disclosure. Always glad to connect with fellow researchers and practitioners in penetration testing and AI security.
- Name:Hrishikesh Patra
- Alias:Hrishikesh7665
- Email:

- Age:22+
- From:Chandannagar, WB, India
4 +
Years Experience
16+
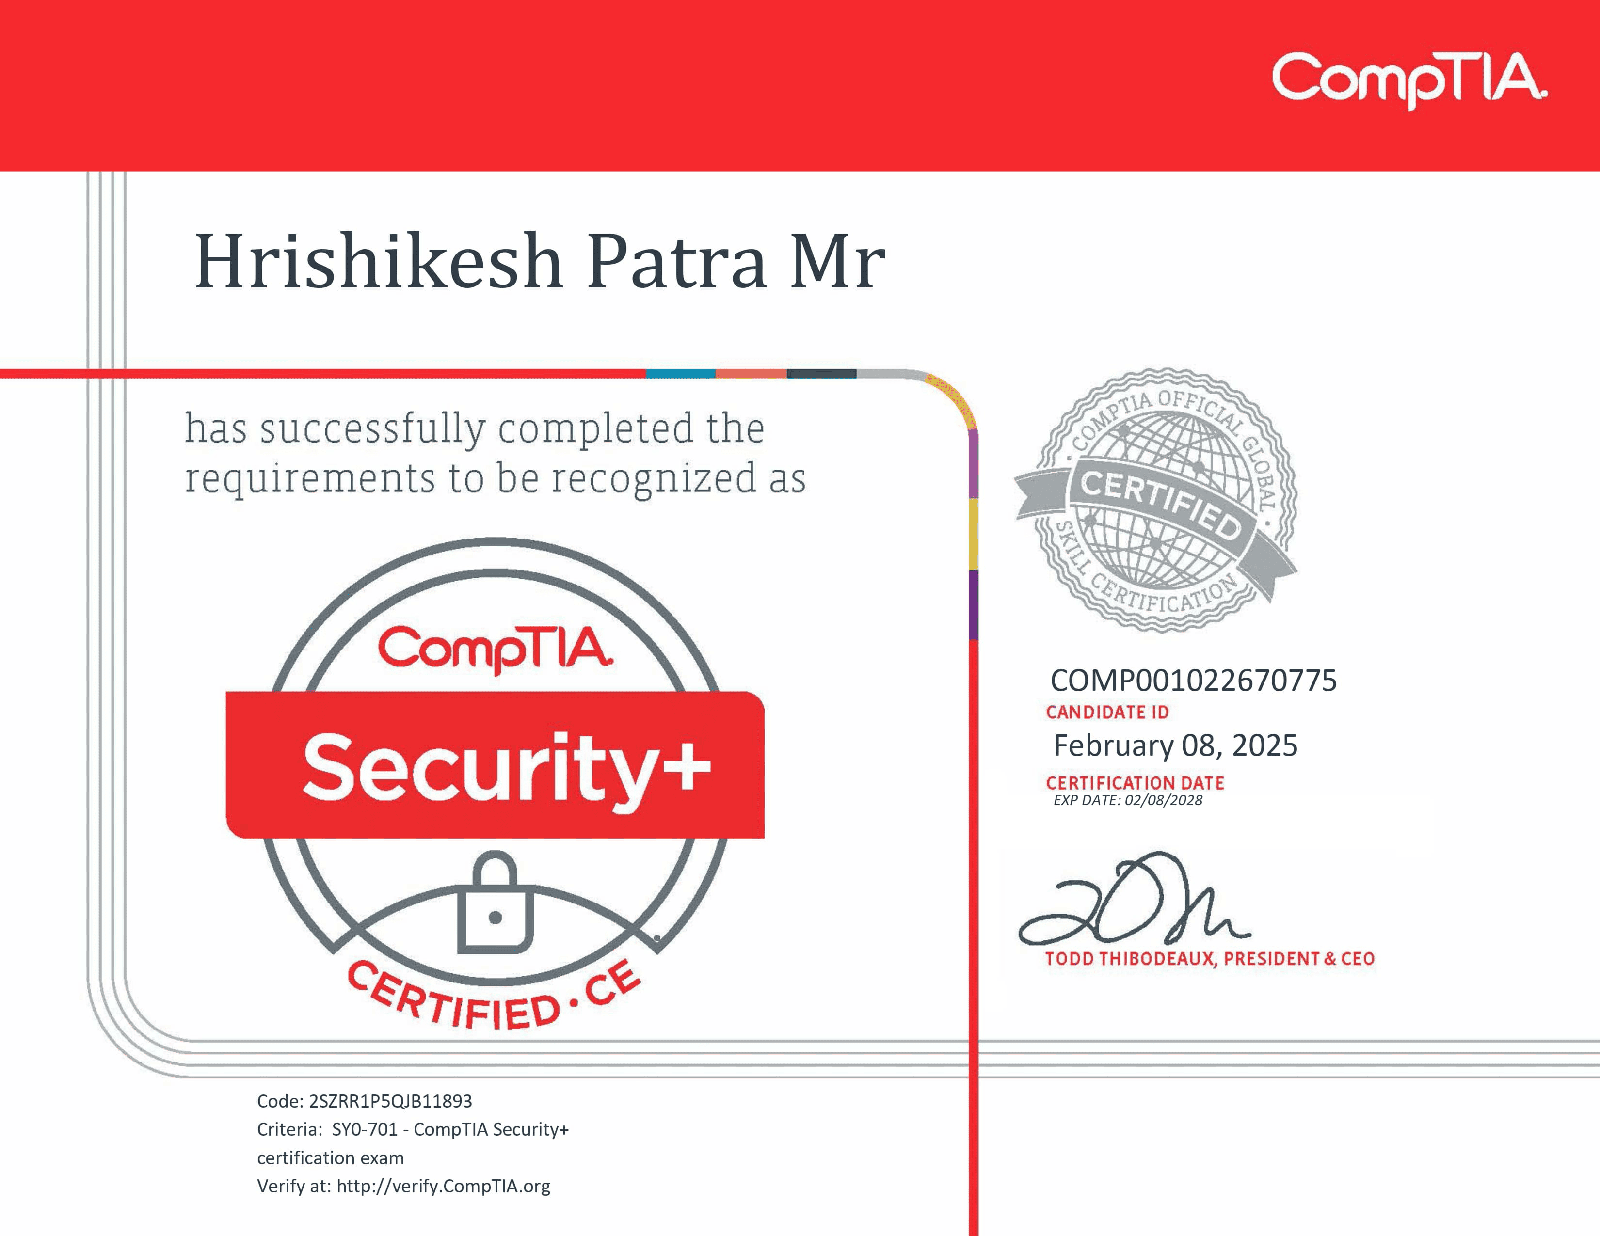
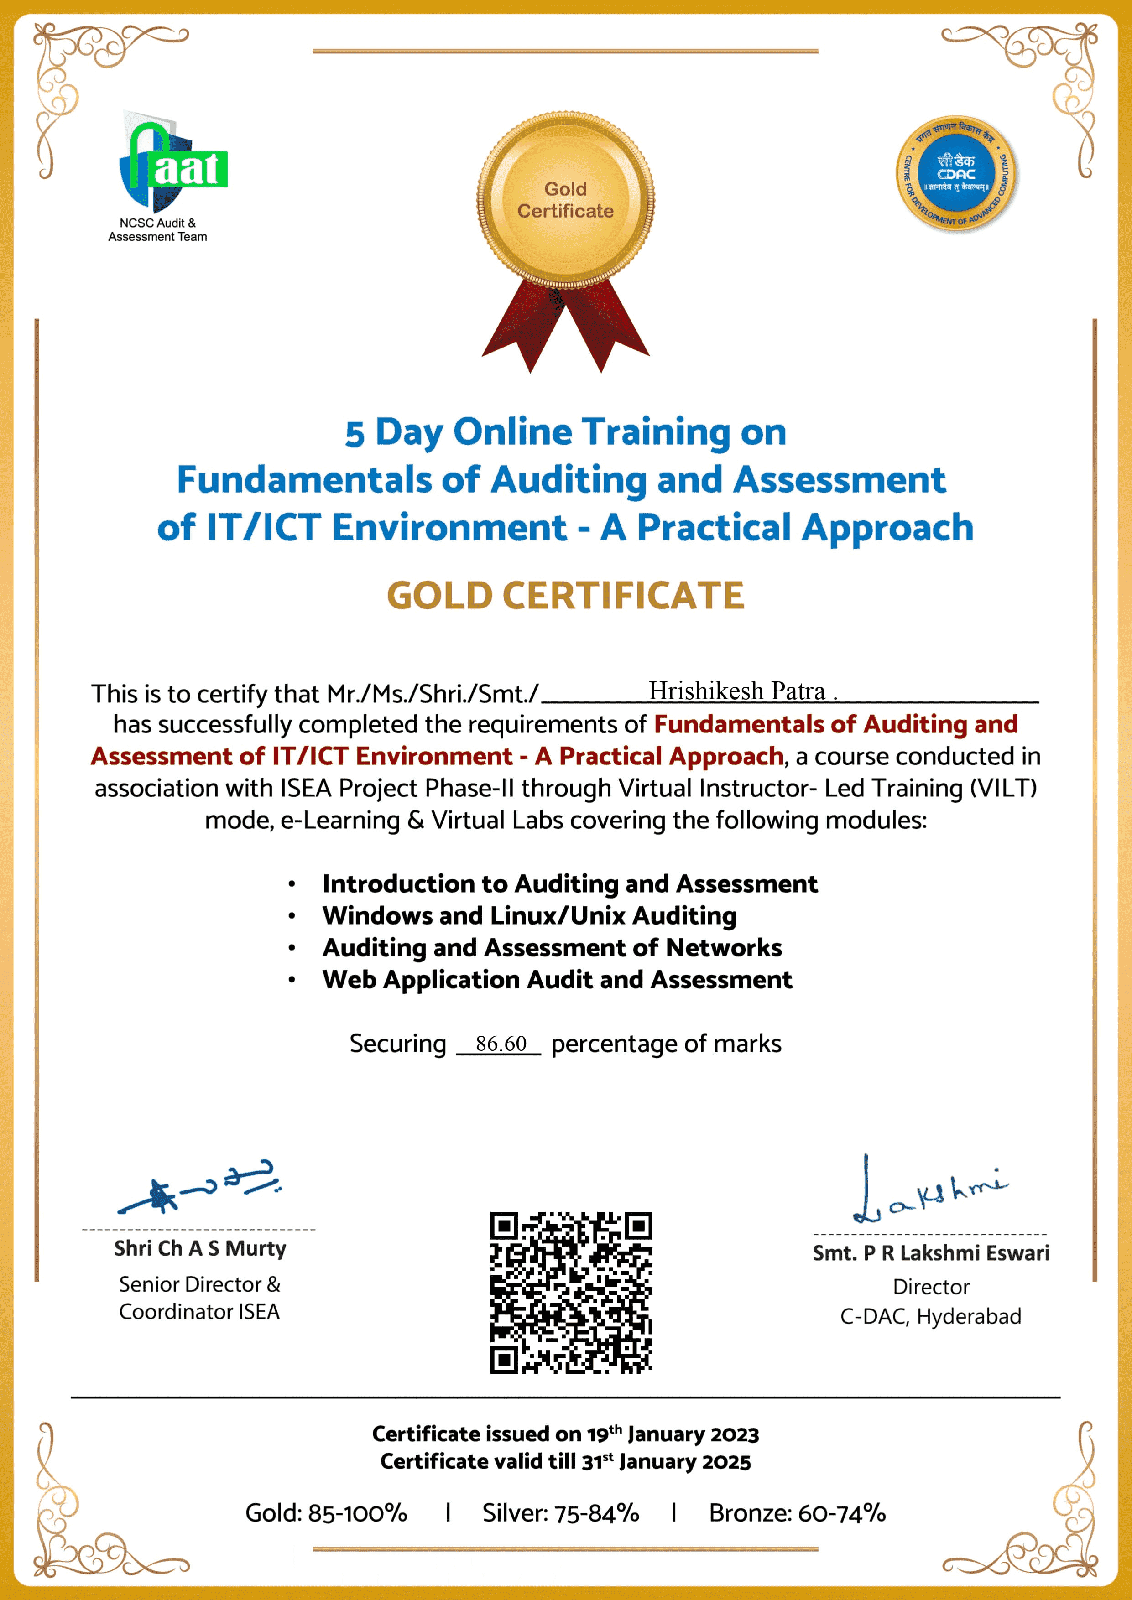
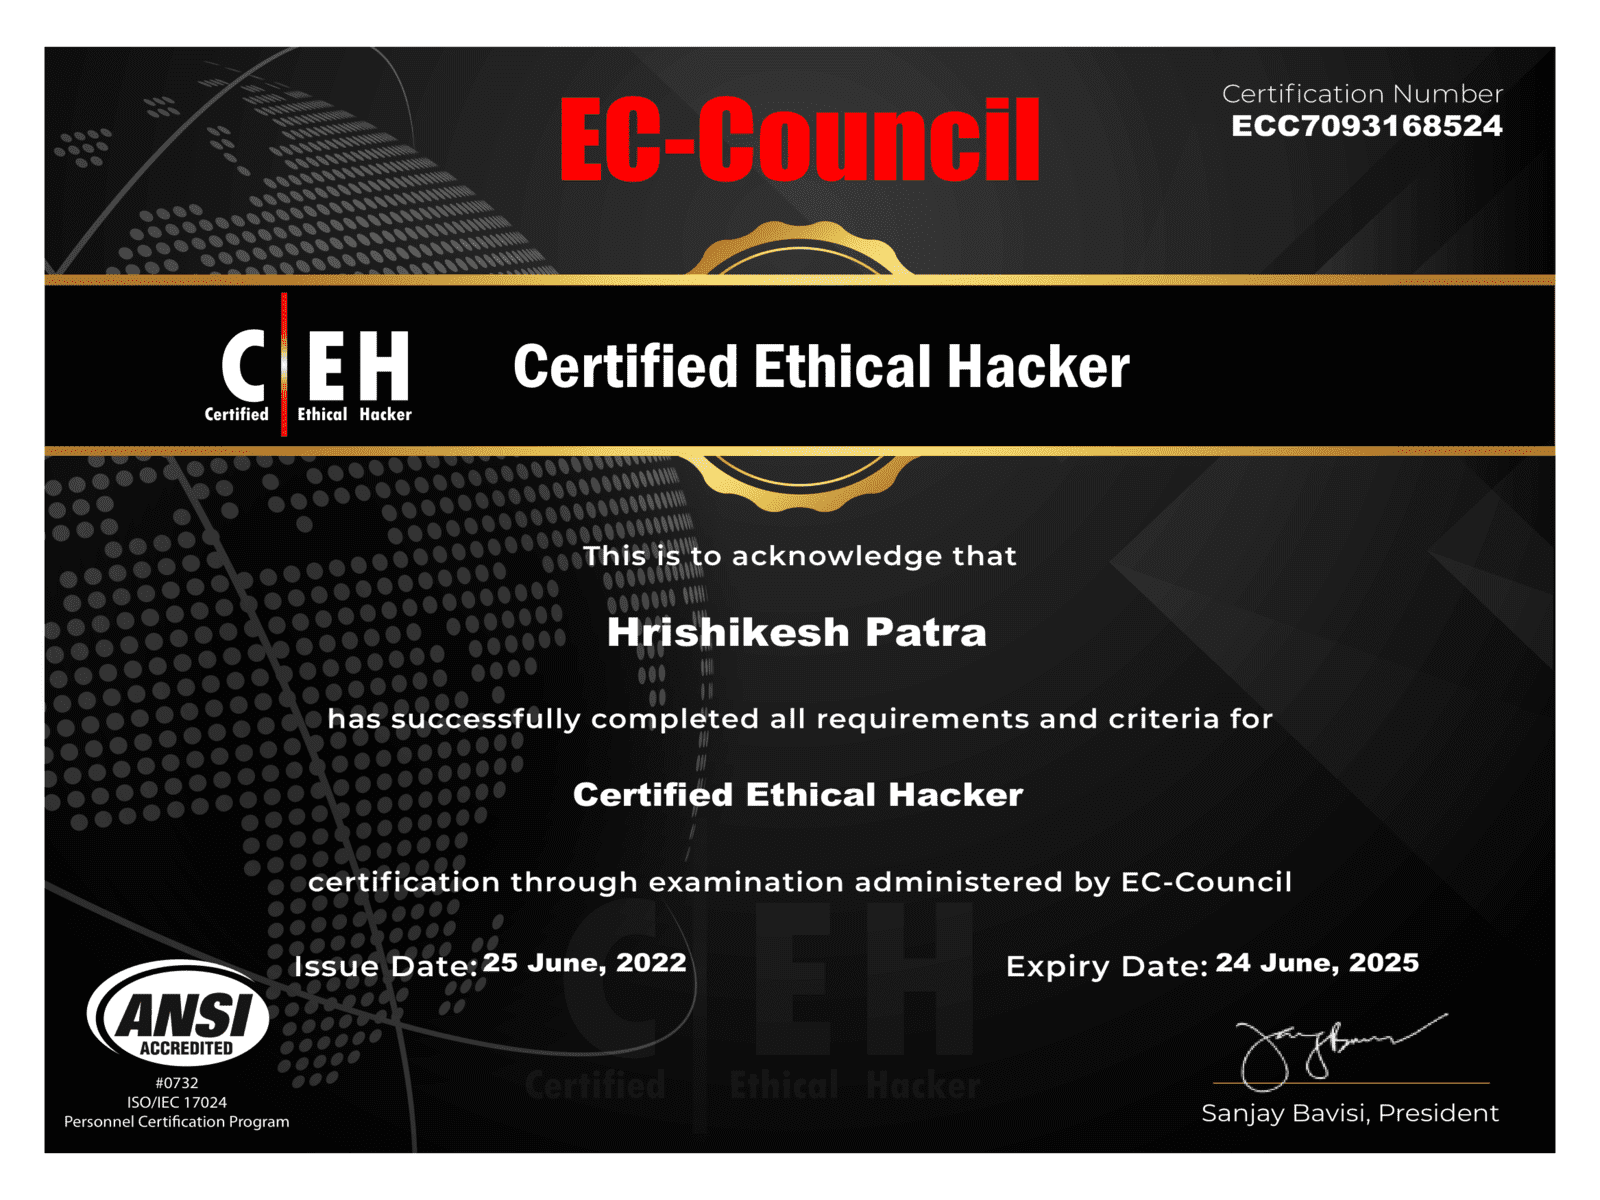
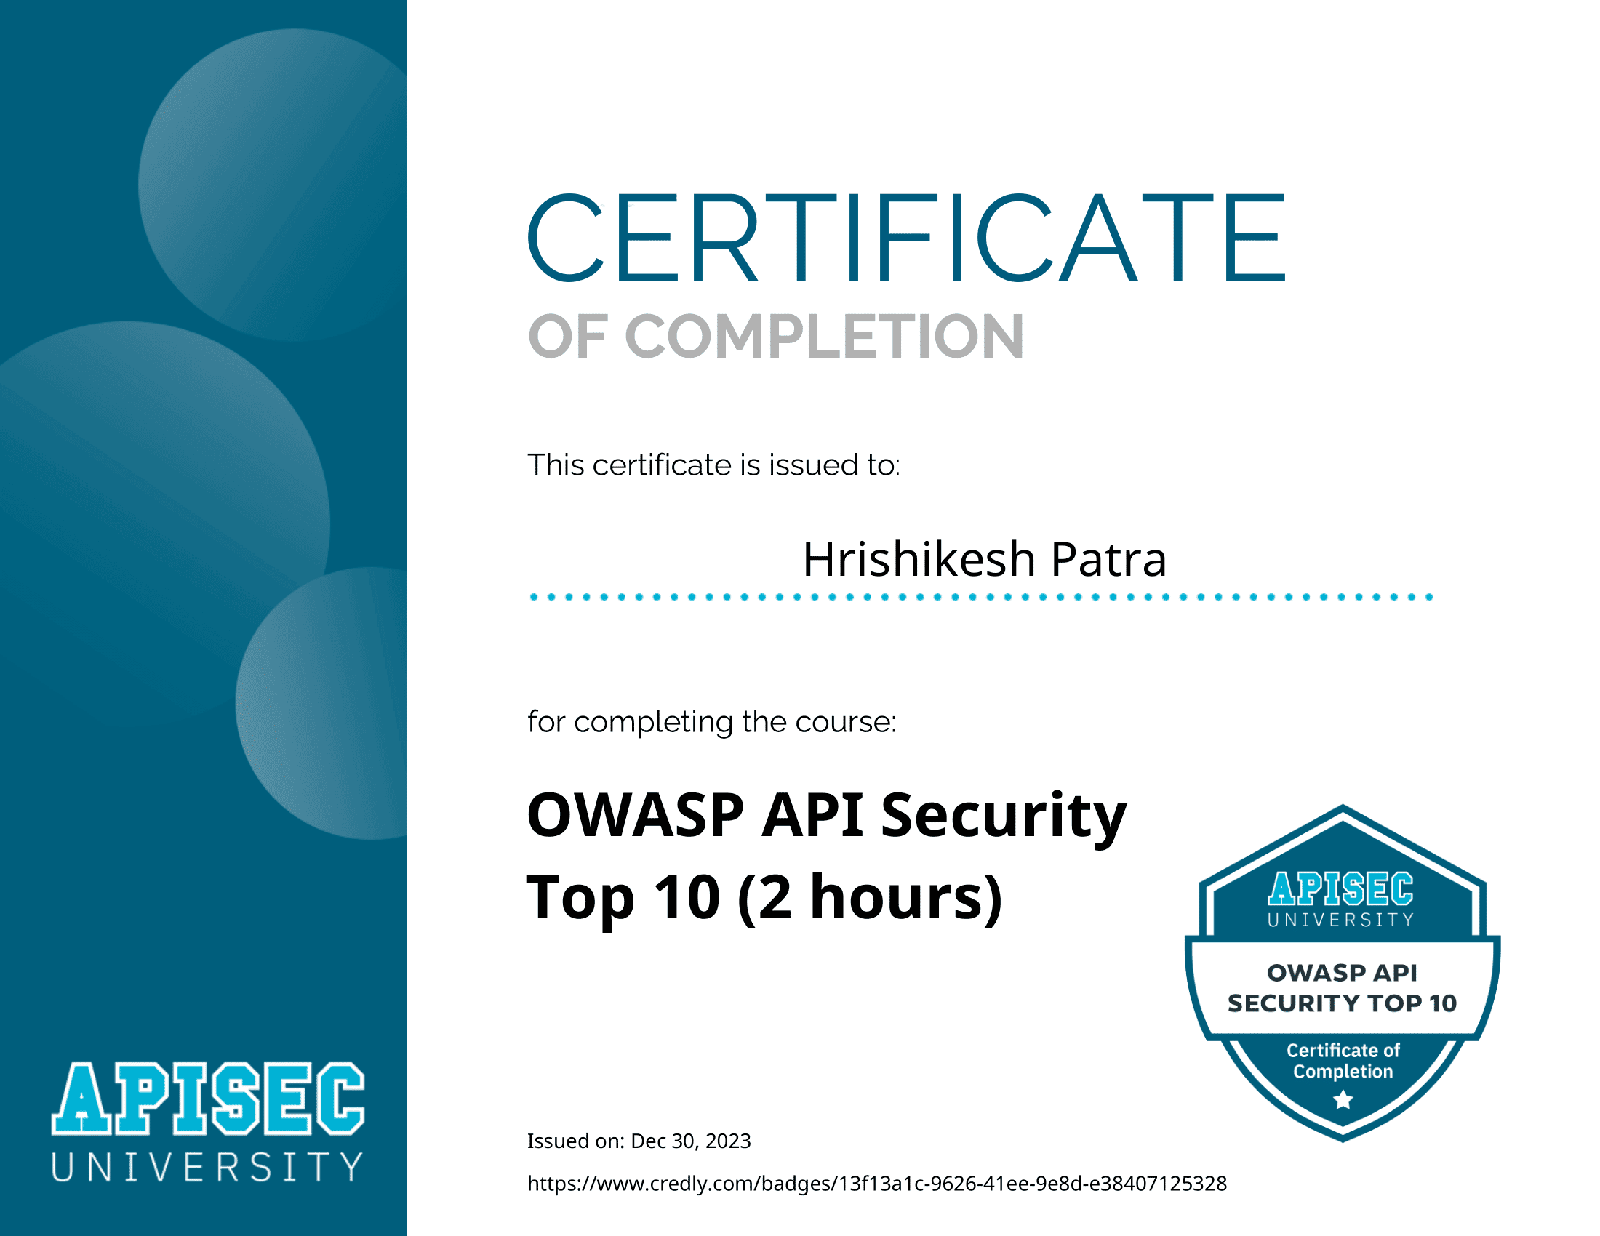
Certificates
200+
Hours of Courses
8+
Projects Done
Resume
Profile
Experience
Ernst & Young Global Delivery Services (EY GDS)
Kolkata, West Bengal, India
Security Consultant 3 – Penetration Testing
March 2026 - Present
- Performing black-box and grey-box penetration testing across web applications, REST/GraphQL APIs, and mobile platforms for banking, telecom, and media clients, aligned with OWASP Top 10 standards and backed by CVSS-scored, PoC-based remediation guidance.
- Developing ProbIQ, an AI-powered Burp Suite extension for automated crawling, stateful application analysis, and attack-path suggestion, now adopted across EY's penetration testing engagements beyond my own, earning a Squad Extraordinaire award.
- Designing and building a production-track autonomous AI penetration testing agent and testing harness under SME guidance, earning a GDS Impact Award and User Recognition.
Security Consultant 2 – Penetration Testing
February 2025 - March 2026
- Delivered end-to-end web application and API penetration tests for enterprise banking, telecom, and media clients, owning scoping, authorization checks, and remediation verification through structured re-testing with dev teams.
- Automated PoC evidence collection and built 20+ Docker-based CTF labs for new-hire skill assessments, cutting manual testing effort across the team.
- Identified Critical, high-business-impact vulnerabilities for enterprise clients, earning two GDS User Recognition awards and a Squad Extraordinaire award for team contributions.
RECOGNITIONS AT EY GDS
- GDS Impact Award, for scalable security automation, including an AI-powered Burp Suite extension
- GDS User Recognition ×3, for security automation, critical vulnerability findings, and cross-account technical contributions
- Squad Extraordinaire ×2, for the AI pentesting harness and Charter red/blue team testing contributions
- Achiever Extraordinaire, for internal automation tooling, including Sabre and the Excel-to-AttackForge converter
Centre for Development of Advanced Computing (C-DAC)
Deputed by ManpowerGroup Pvt. Ltd.
Kolkata, West Bengal, India
Assistant Information Security Analyst
May 2023 - February 2025
- Promoted for consistent performance with expanded security assessment responsibilities across web, API, and Android platforms.
- Identified and remediated Critical and High-severity vulnerabilities, including RCE and payment-bypass flaws, across 50+ government web, REST API, and Android applications.
- Built System-Scrutinizer, a Python and PowerShell tool that automates CIS benchmark checks with detailed HTML reporting, and led a 50+ challenge CTF platform that trained 300+ participants; implemented ISMS-aligned security controls.
Information Security Associate
March 2022 - April 2023
- Conducted web, REST API, and Android mobile security testing for government systems.
- Performed CVSS scoring and threat modeling to deliver prioritized, developer-actionable remediation guidance.
- Supported network infrastructure security assessments, strengthening baseline security controls across government client environments.
Vulnerability Research & Recognition
Top 15 NCIIPC RVDP Researcher (×2)
Ranked in the Top 15 of 426 researchers in NCIIPC's Responsible Vulnerability Disclosure Program (Q3 2023 & Q1 2024) for identifying vulnerabilities across 50+ government web applications.
CERT-In Acknowledgement
Acknowledged by India's CERT-In for responsible disclosure of security vulnerabilities in multiple public-facing government web applications.
Education
August 2022 - July 2024
Master of Computer Application
JAIN (Deemed to be University)
Full-time MCA - CS and IT (Online Mode)[UGC & AICTE Approved]
Acquired skills of Web Development, Python, PHP, Networking, DBMS, Computer Programming, Project management, etc.
Grade: A (9.04 CGPA), Distinction
November 2019 - December 2022
Diploma
Indian School of Ethical Hacking (ISOEH)
Diploma in Cybersecurity
Acquired skills of C, Python, Networking, Cybersecurity, Ethical Hacking, Penetration Testing, etc.
Grade: A+
July 2019 - July 2022
Bachelor of Commerce (B.Com)
University of Burdwan
Chandernagore Government College (Duplex College)
Grade: A (7.41 CGPA)
Passing Year - 2019
Higher Secondary
West Bengal Council of Higher Secondary Education
Kanailal Vidya Mandir (English Section)
Grade: A (71.2%)
Passing Year - 2017
Secondary
West Bengal Board of Secondary Education
Kanailal Vidya Mandir (English Section)
Grade: A (62%)
Skills Summary
Penetration Testing
Web App VAPT API Pentesting (REST & GraphQL) Android / Mobile Pentesting Network Pentesting Black / Grey-Box Testing Vulnerability Assessment CVSS Scoring
Standards & Frameworks
OWASP Top 10 OWASP API Security Top 10 OWASP Mobile Top 10 CIS Benchmarks Threat Modeling OAuth 2.0 & OpenID Connect JWT
Tools & Platforms
Burp Suite OWASP ZAP Metasploit Nmap Nessus MobSF Drozer Frida ADB APKTool Postman Docker Kali Linux
Languages & Reporting
Python PHP JavaScript SQL Bash Git ISMS VAPT Report Writing
AI Security
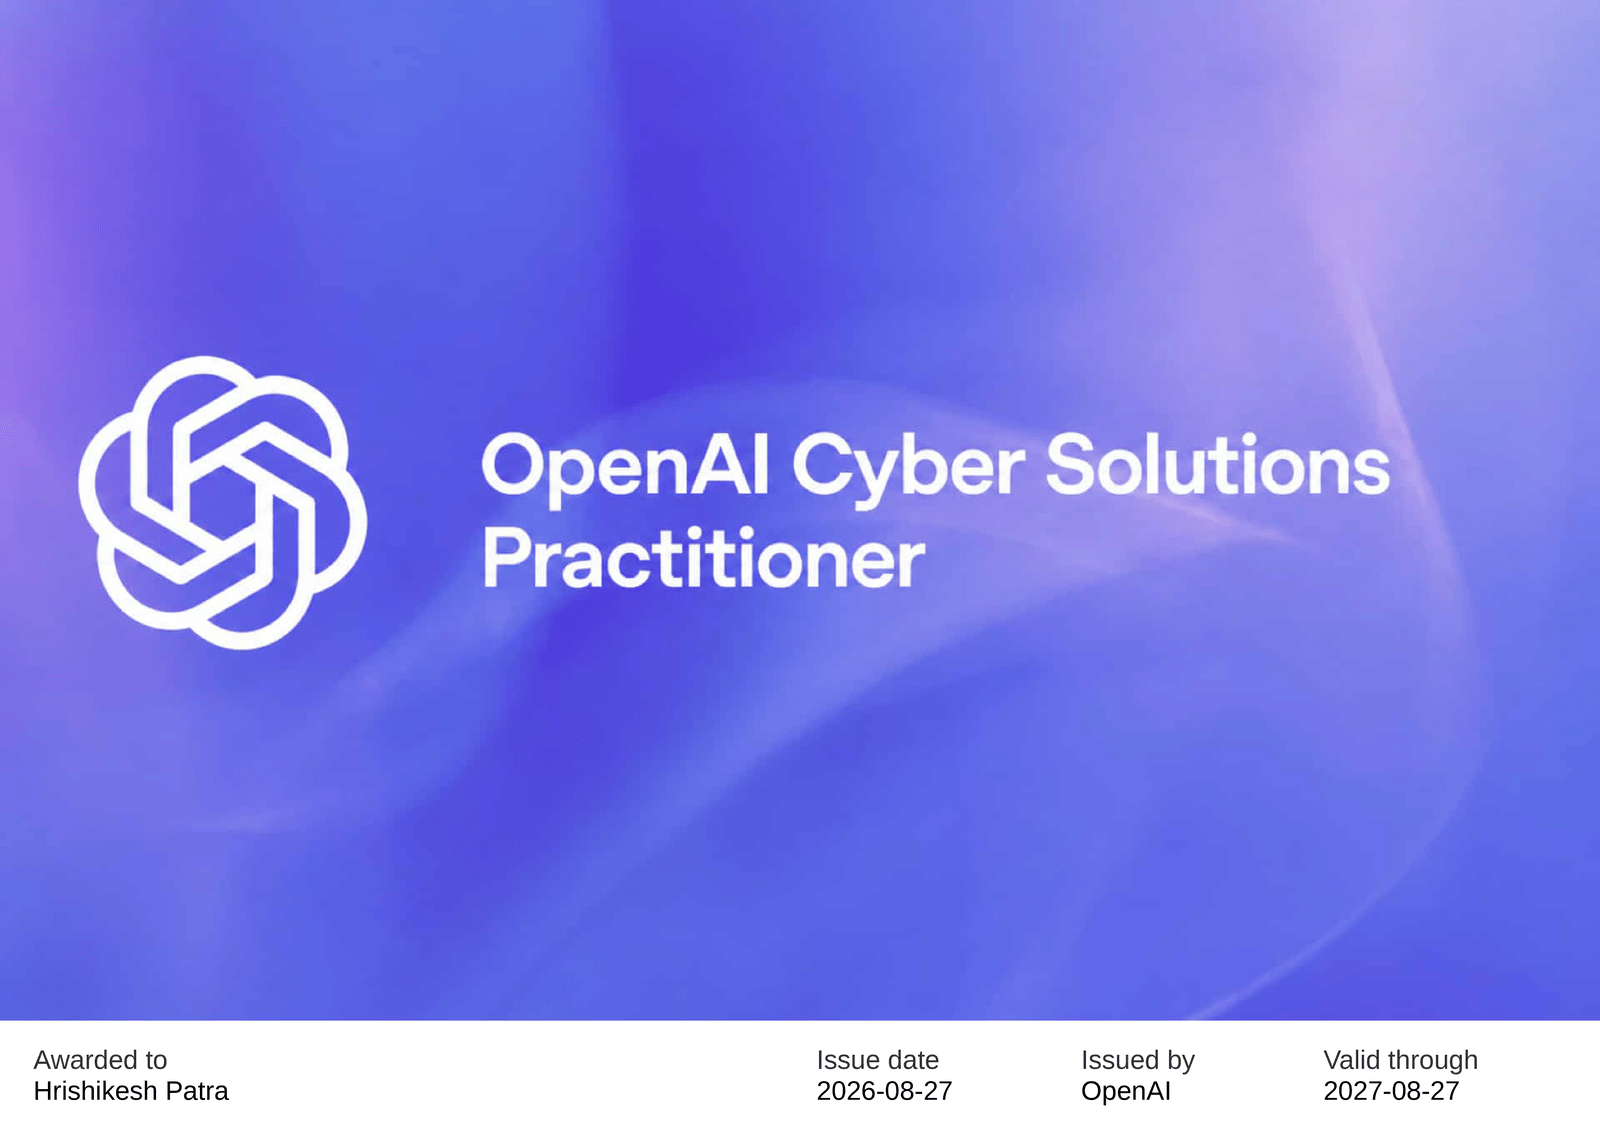
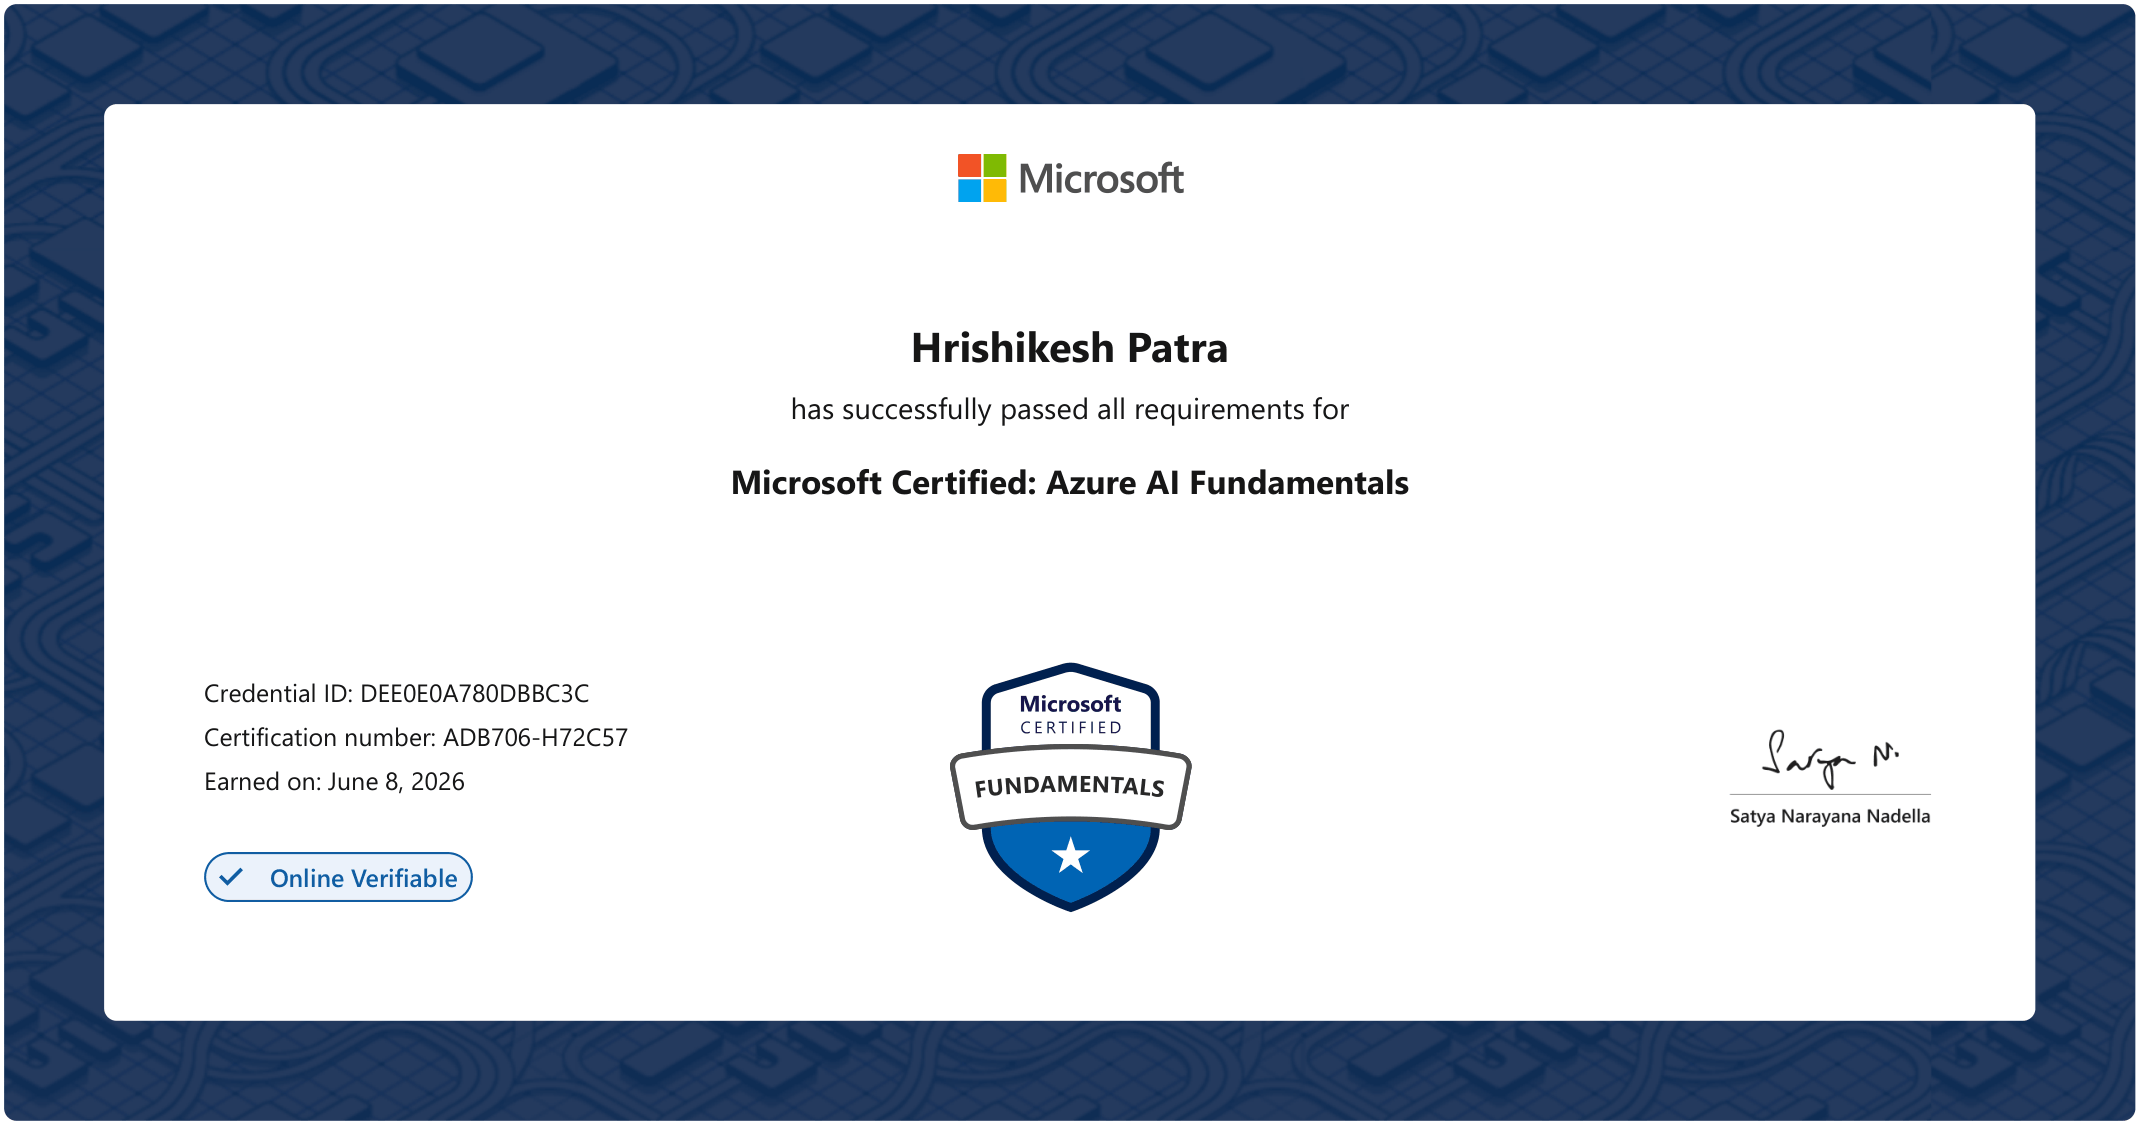
AI/LLM Security Prompt Injection Testing AI Agent Security Generative AI Risk Assessment Burp Suite Extension Development Azure AI Fundamentals









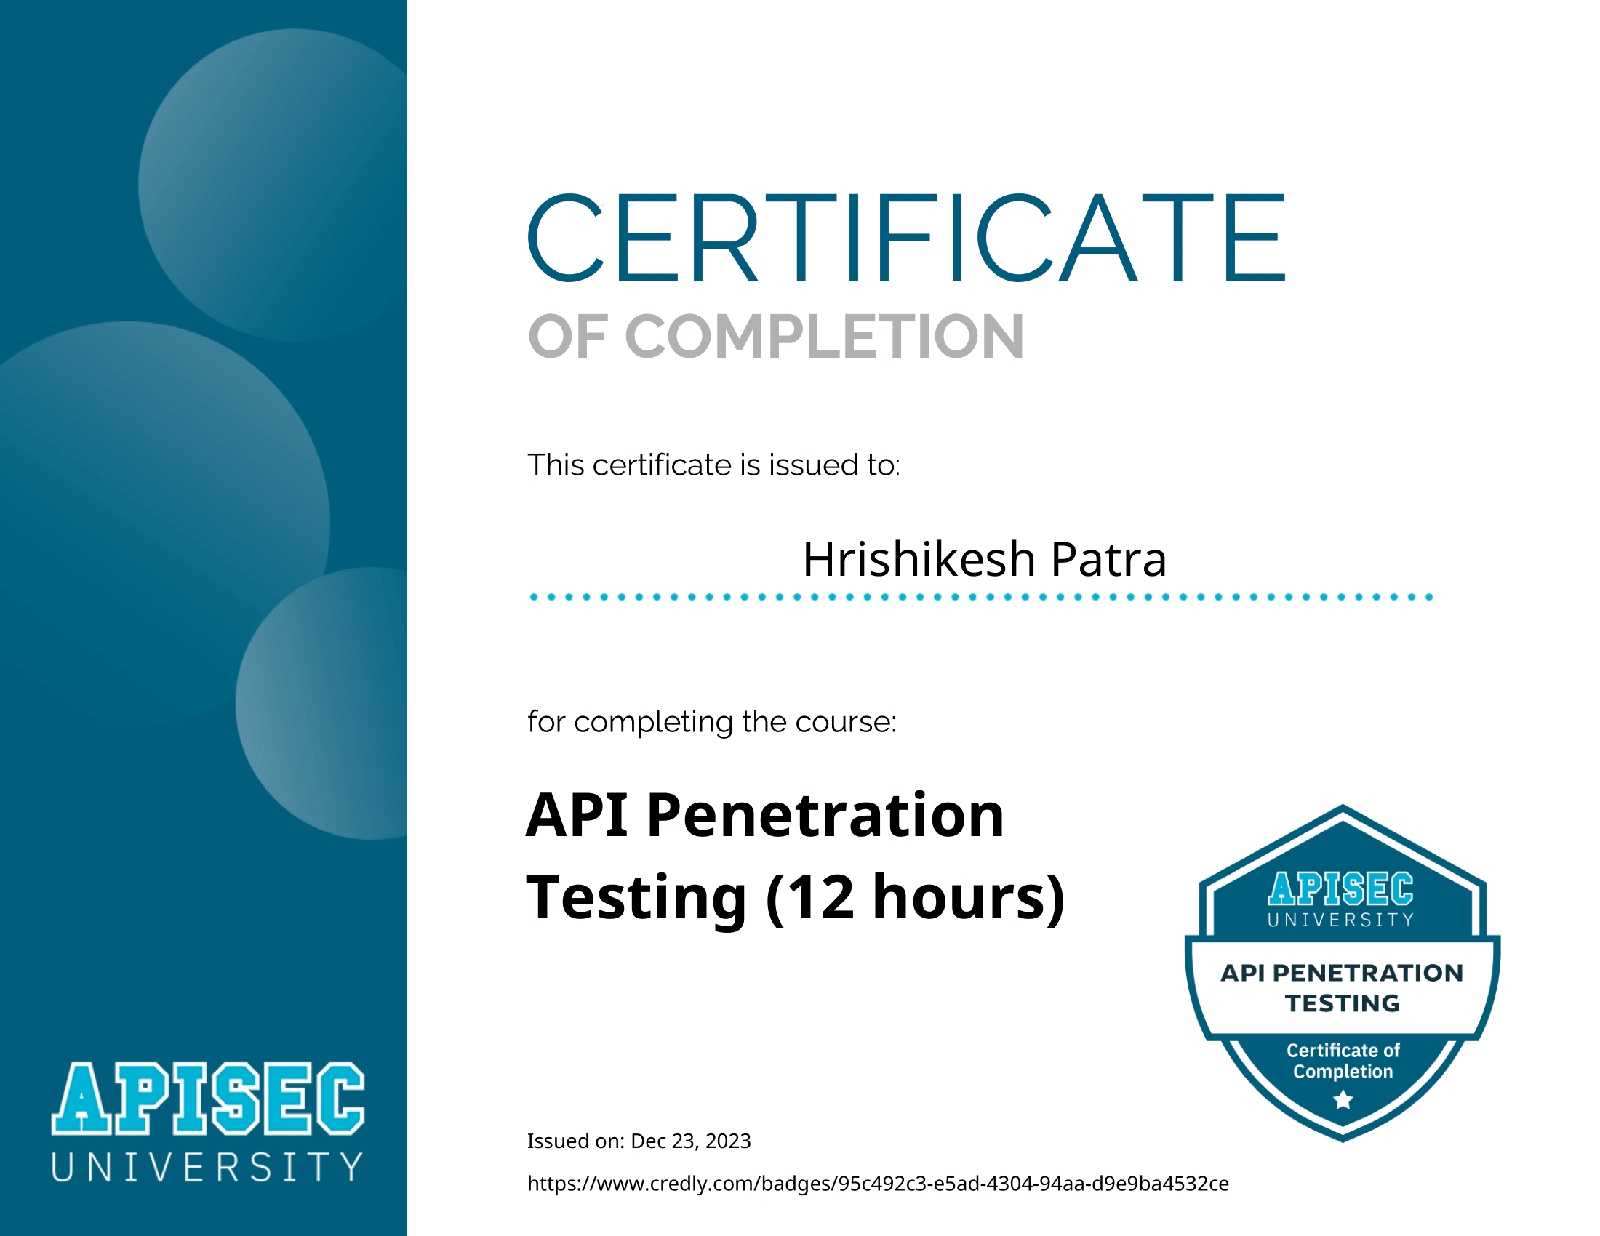
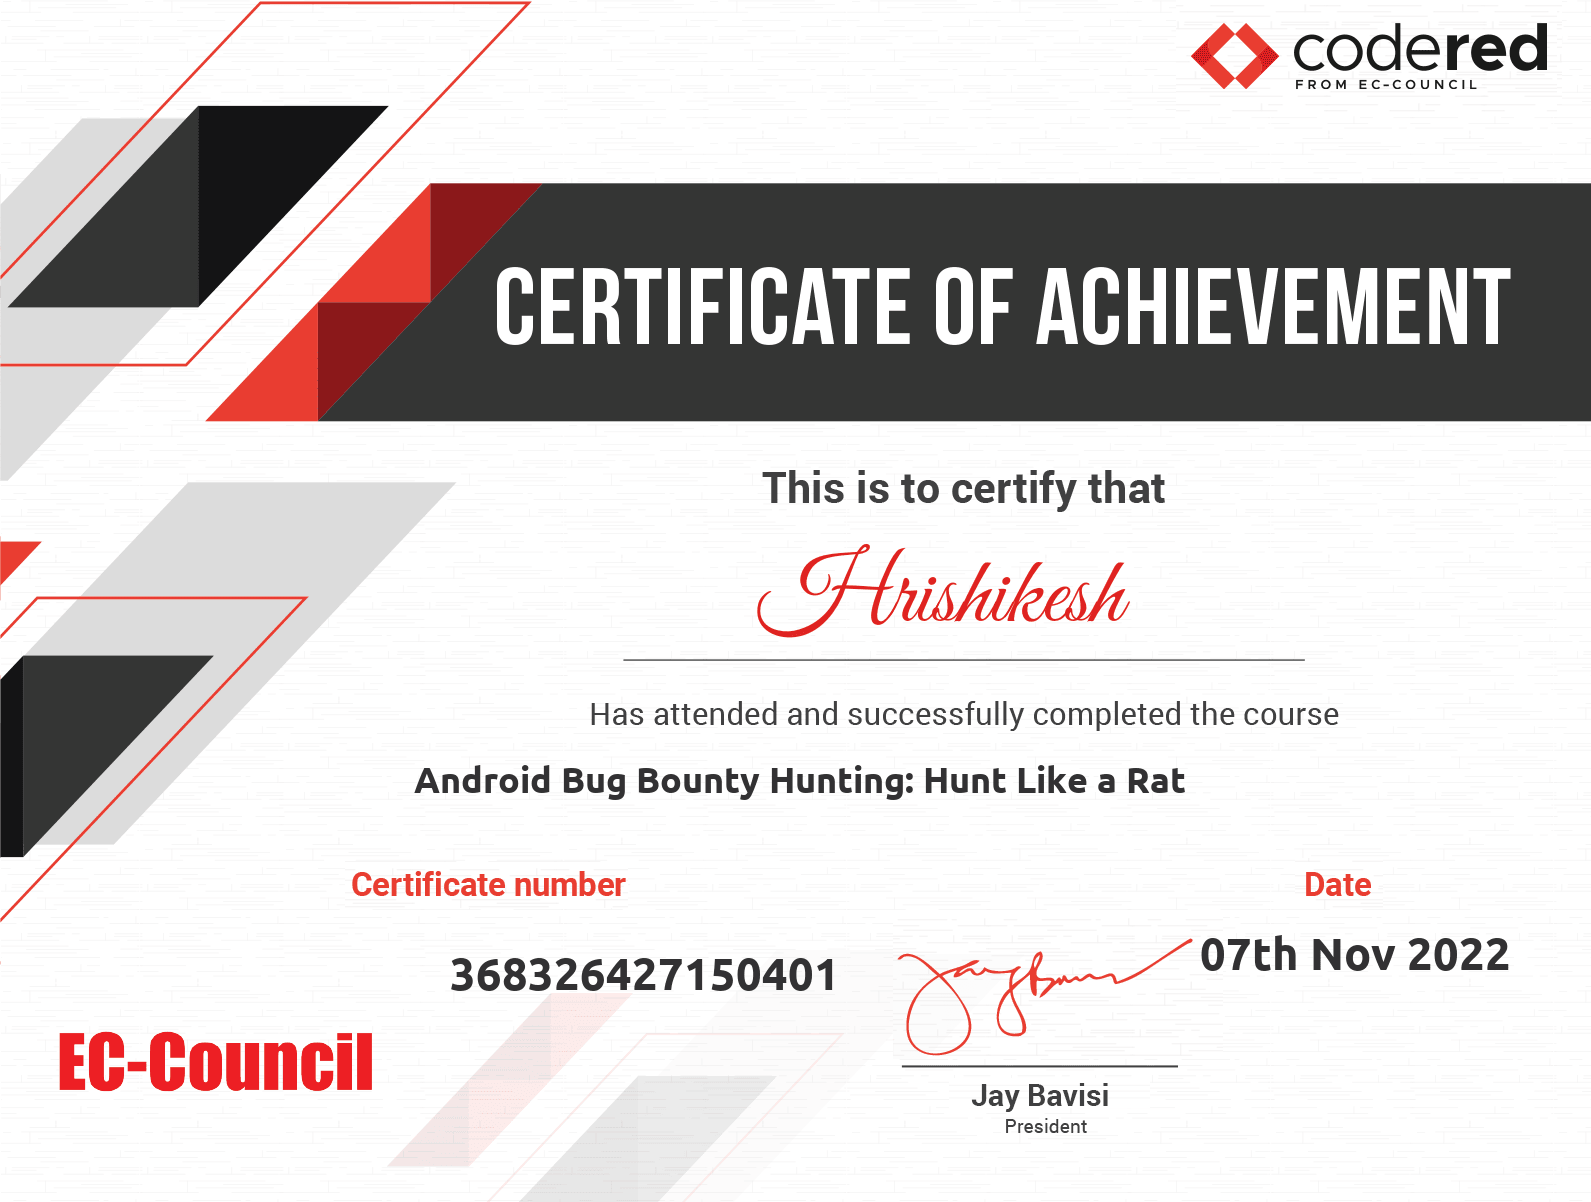
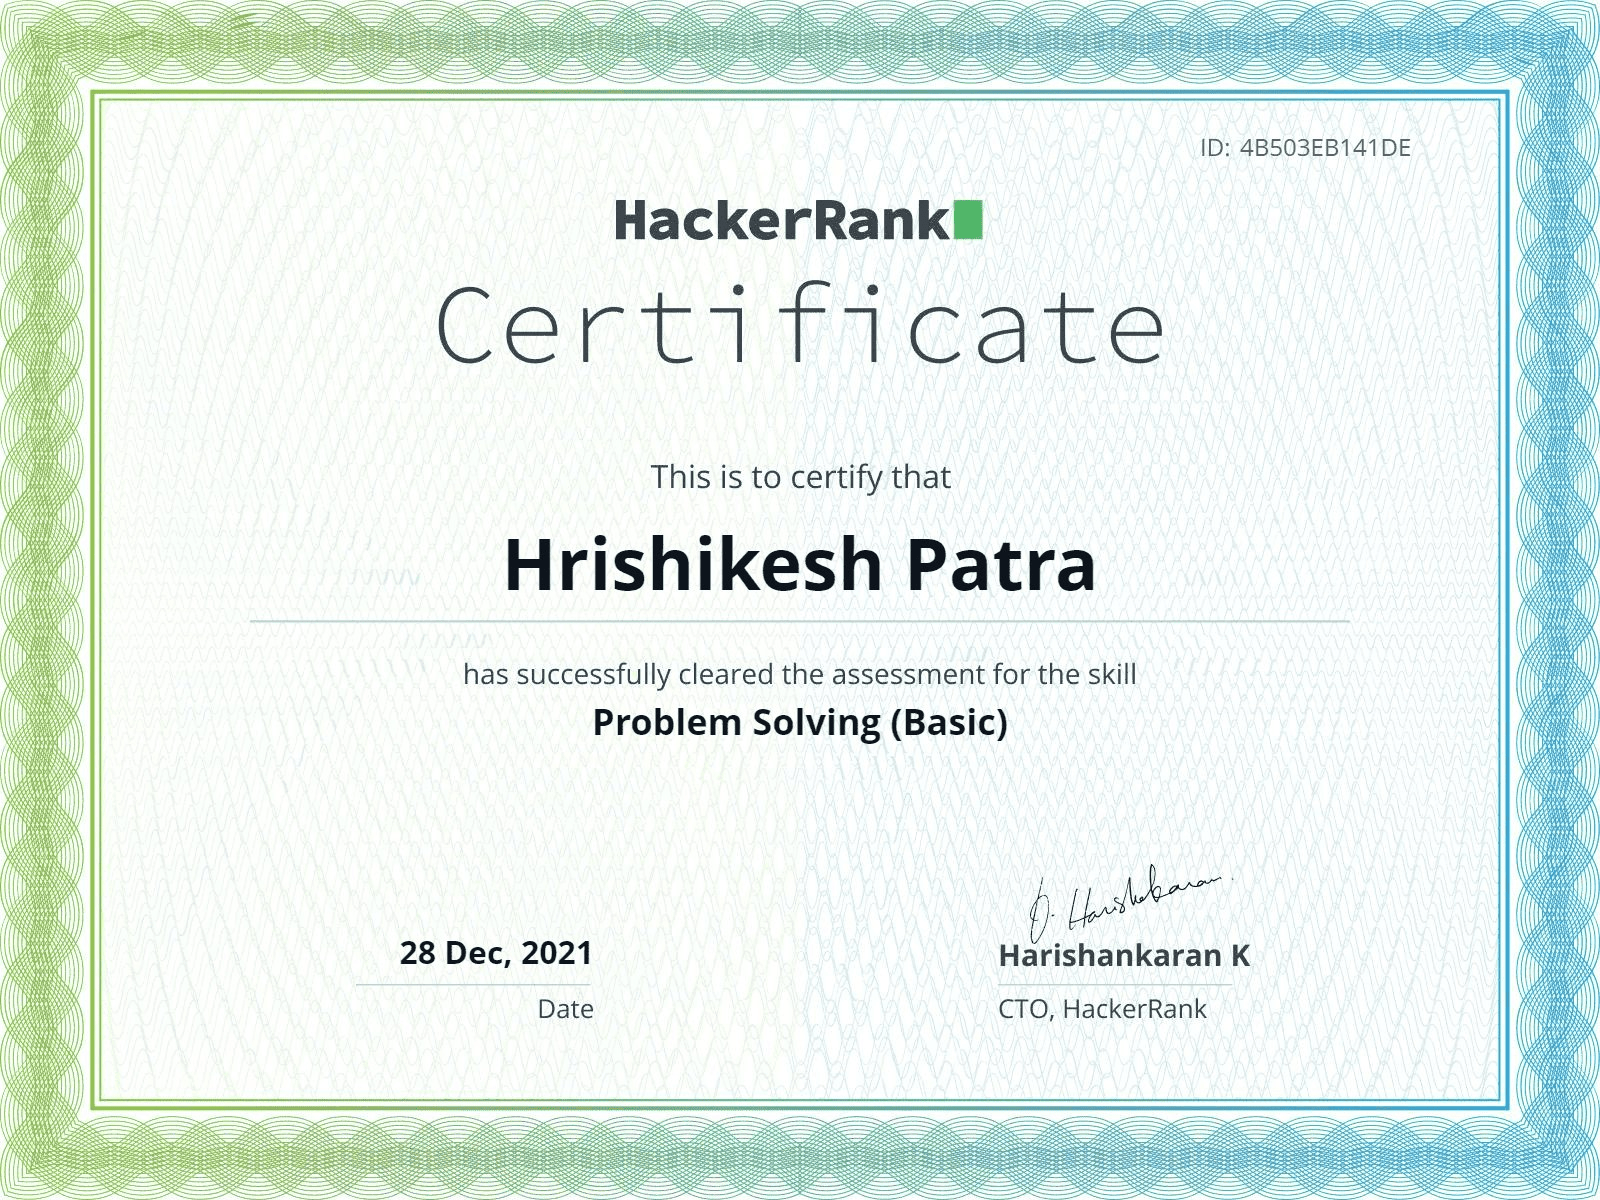
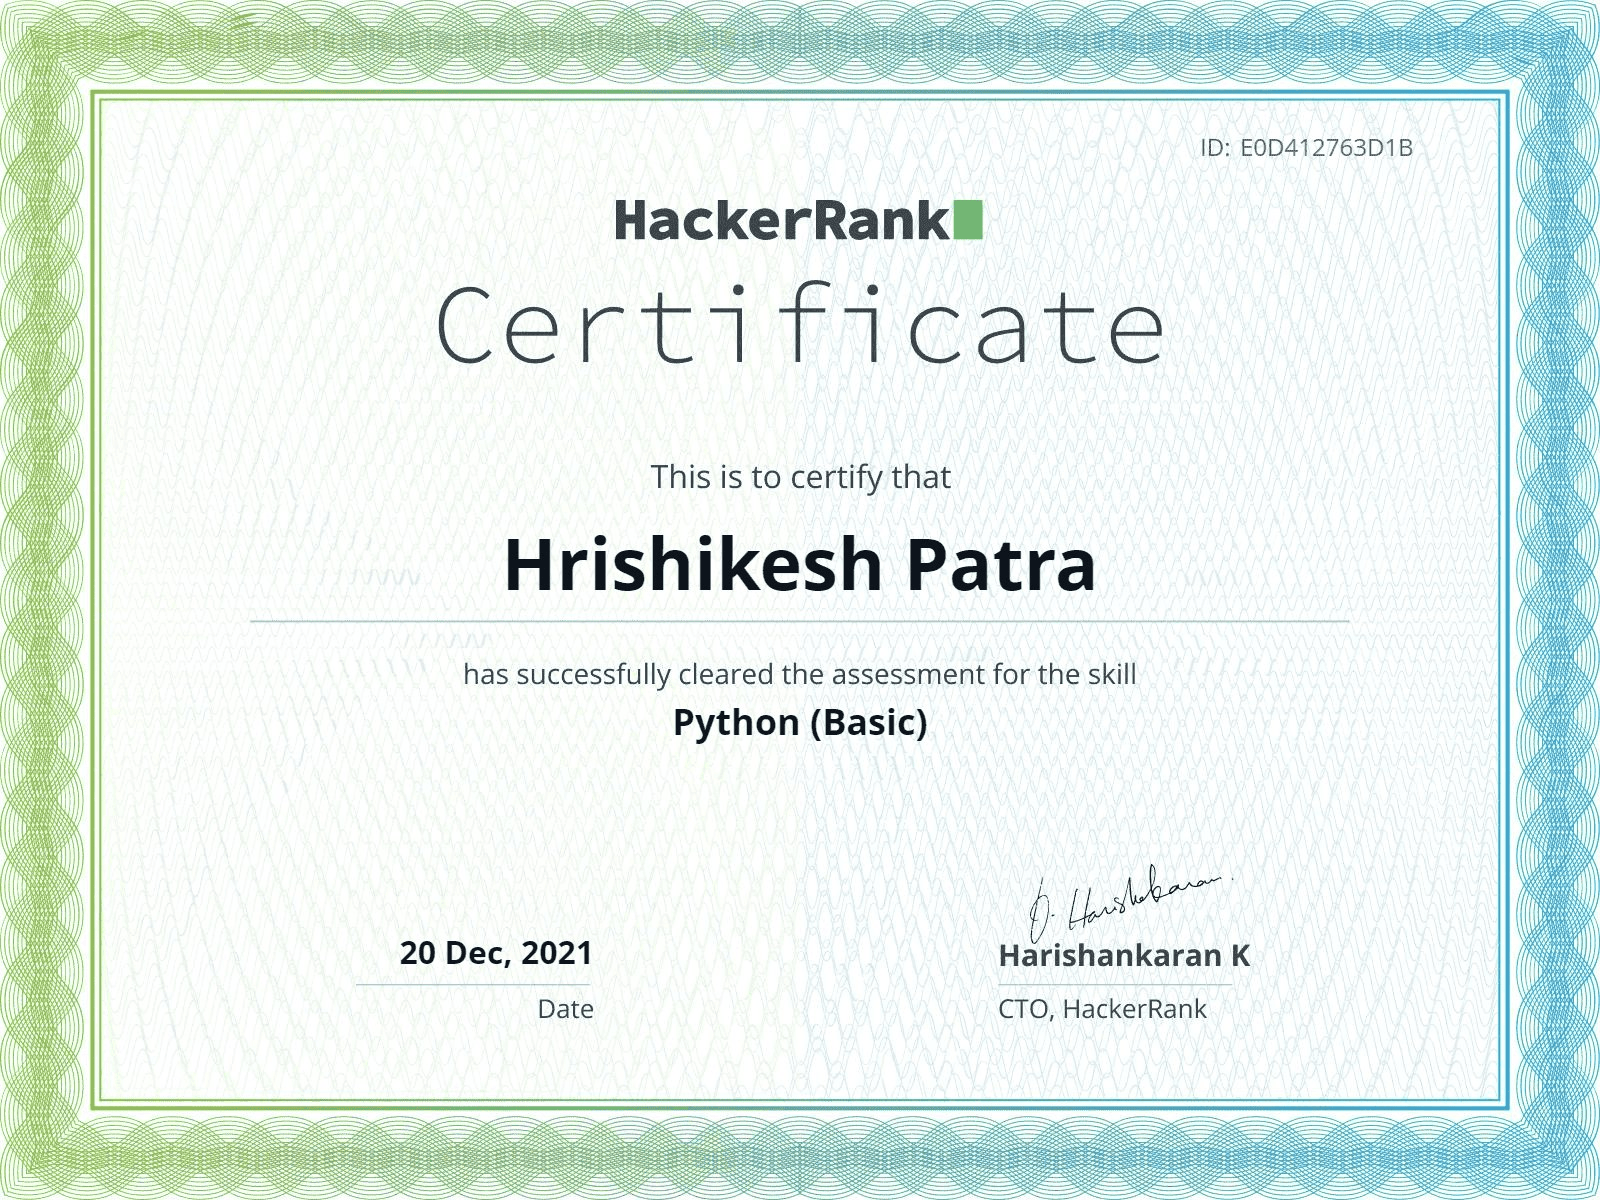
Certificates
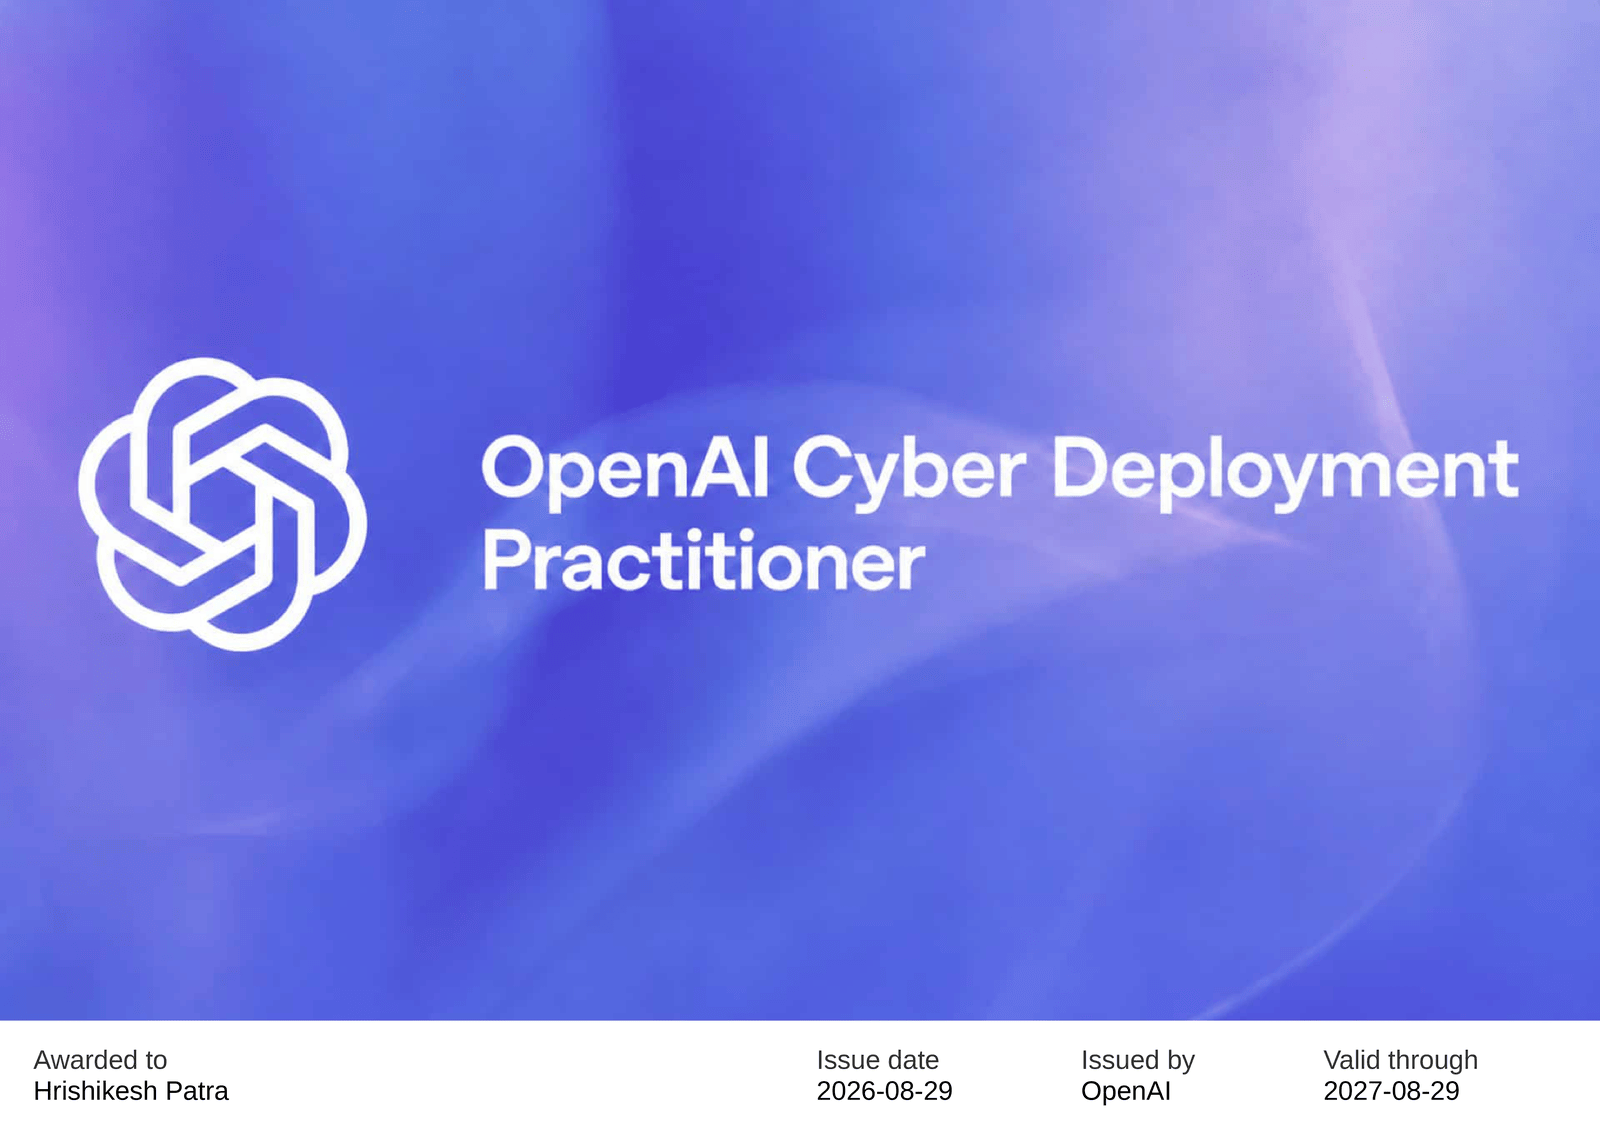
Credentials
Interests
Avocations
Automation
I look for ways to make security testing more efficient, from automating evidence collection to exploring AI-driven automation for faster triage.
AI Pentesting
AI security is an area I'm actively growing in, testing AI-based applications for risks like prompt injection and contributing to an autonomous AI pentesting tool.
Pentesting
I enjoy hands-on testing across web applications, REST and GraphQL APIs, Android apps, and AI-based systems, looking for where real behavior doesn't match intended design.
Open Source Contribution
I contribute to various open-source security projects, with one major contribution to FLARE VM, alongside sharing my own tools with the community.
Custom ROM Building
I experiment with Android by building custom ROMs, working with device trees and system-level changes to understand the platform better.
Reverse Engineering
I enjoy reverse engineering applications using tools like APKTool, JD-GUI, and Frida, and apply the same approach across other pentesting work.
Capture the Flag (CTF)
CTFs keep me learning outside of work, playing challenges and building Docker-based CTF labs for hands-on security training.
Malware Analysis
I study malware using static and dynamic analysis in safe, sandboxed environments to understand how threats operate.
Projects
My Works
